CDBConsilium brings business continuity, ICT Readiness for Resilience, information security and NIS2 together in one coherent model. For SMEs and organisations in critical sectors that want to withstand a disruption and pass an audit.
You can't always prevent a disruption. How strong you come out of it is up to you. I'm glad to help you get there.
20+years of experience in BCM and crisis management
30+years of professional experience in IT, technology consulting and implementing BC and InfoSec management systems
6domains in one resilience model
4standards in one control framework: ISO 22301, ISO 27001, NIS2 and ERM
The challenge
Six domains, one organisation
In many organisations, BCM, information security, risk management and crisis management work alongside each other rather than together. Each team has its own policies, controls and reporting. The result is duplicated work, contradictions and weak spots that only show up during a real crisis.
I connect those domains into one resilience model: processes, controls, governance and reporting that fit together. The result is an organisation that is agile, coherent and ready for an audit.
BCMISO 22301
Information securityISO 27001
Risk managementISO 31000, ERM
CybersecurityNIS2, CyFun
PrivacyGDPR
Crisis managementEscalation and communication
One governance, one control framework, one reporting line
Services
Integrated Resilience Services
From a first assessment to a working model with management reporting. You choose the part you need, or the full programme.
Resilience Integration Assessment
A maturity assessment across all domains together. You see overlaps, gaps and missing links.
Maturity score per domain
Quick wins and a strategic roadmap
Resilience Operating Model
The design of how resilience is governed in your organisation.
Governance, roles and RACI
Overarching processes and annual planning
Implementation support
I help departments break out of their silos, with workshops, communication and training.
From plan to working practice
Tailored to your teams and pace
Resilience Cockpit
One management dashboard that brings together BCM, cyber, risks, incidents and maturity.
For the board and risk committees
KPIs and KRIs that drive decisions
Integrating NIS2, ISO 27001 and ISO 22301
Compliance frameworks that work together instead of side by side.
One harmonised control framework
Mapping matrix and audit-ready file
Also available separately
Need just one specific piece? That works too.
Business impact analysisContinuity plansICT Readiness for ResilienceNIS2 and CyFun readinessCrisis exercises
Approach
How we work
A clear four-step path, with tangible results after each step.
Step 1
Measure
We map your current maturity across all domains, through interviews and document analysis.
Step 2
Design
We define governance, processes and a shared control framework, aligned with your risk appetite.
Step 3
Implement
We put the model into practice: plans, procedures and reporting your teams actually use.
Step 4
Test and improve
Exercises and reviews show whether it works. What we learn feeds back into the model.
Results
What you actually get
Results you can present to your board, your auditor and the regulator.
Gap analysis report
Maturity score per domain, overlaps and contradictions, quick wins and a roadmap.
Operating model
Governance, roles and responsibilities, process flows and reporting structure.
Resilience dashboard
A visual cockpit for the board and the risk committee.
Control framework
Harmonisation of ISO 22301, ISO 27001, NIS2 and ERM, with mapping matrix and audit file.
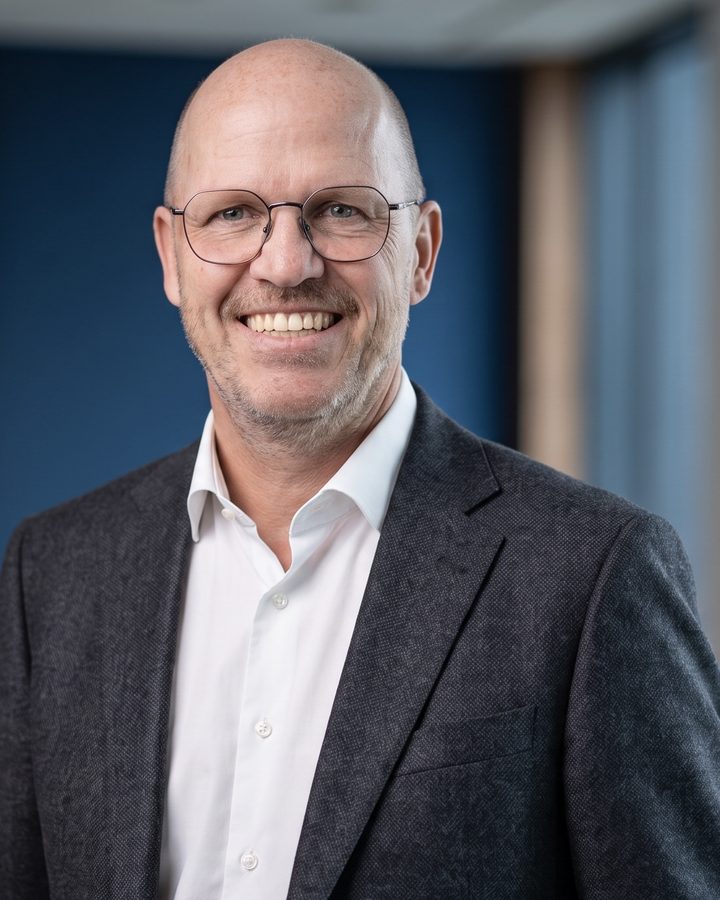
Chris De Blende
Business Continuity, Resilience and GRC expert, founder of CDBConsilium
I have been working in business continuity, crisis management and recovery for more than twenty years. My career started in IT: as a system and network administrator, later as IT Operations Manager and IT Service Manager at PwC. Continuity then became my profession, as a BCM consultant and as a Business Continuity and IT Service Continuity expert at Ypto and Proximus, among others.
That combination makes the difference. I understand how your business processes depend on IT, suppliers and the cloud, and I translate regulations such as NIS2 and CyFun into measures that work in practice. I work "people first": I bring business and IT to the same table, and make sure your teams can carry the model themselves.
Since 2024, through CDBConsilium, I have been helping SMEs and organisations in critical sectors become more resilient: with BIAs, continuity and recovery plans, crisis exercises, NIS2, CyFun and ISO 27001 assessments, and GRC roadmaps.
What I'm good at
Seeing the big pictureOpen-minded and keeping the overview however complex things get, with a pragmatic approach and respect for others.
Getting people movingStrong at motivating and teamwork, solution-oriented and eager to learn.
Planning aheadProactive planning and continuous improvement, rather than waiting for things to go wrong.
Staying currentI closely follow cyber threats, regulation, trends and technology.
Contact
Let's talk
Email or call me and tell me briefly where your organisation stands. I'll reply with a proposal for a first, no-obligation conversation.